An e-signature link proves that someone held the email, and an access code adds a shared secret on top. Pactly e-Sign now offers a second layer of identity proof: under Signer identity, choose Require Pactly login and each recipient must sign in as themselves before the document opens. A forwarded link stops at the point of signing, because the person holding it cannot authenticate as the intended recipient.
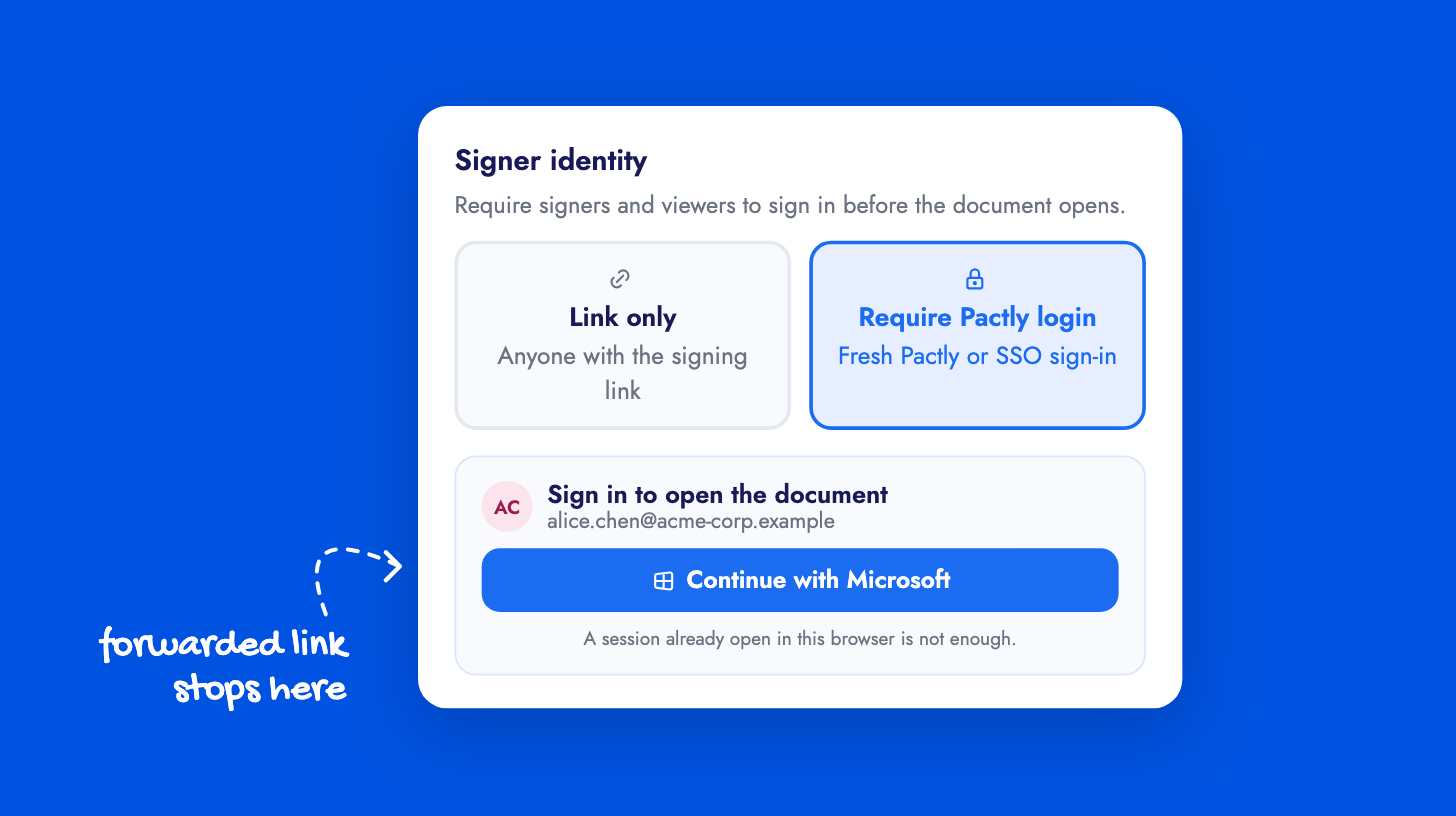
This is strongest for organizations on single sign-on. A recipient completes a fresh sign-in with their identity provider, so the signature is tied to an identity your company already governs, with its own MFA and account controls. A session already open in the browser is never accepted, and anyone signed in to a different account is asked to log out first. If your company allows Just-In-Time provisioning, a colleague without a Pactly account yet can still be added, as long as their email is on one of your verified domains, and the account is created only after their first verified sign-in.
The method used is written into the audit trail and the audit certificate, so a compliance response can cite exactly how each signer was verified. The option is available when every signer and viewer on the request can sign in, and Pactly names anyone who cannot. The signature request guide covers the signer identity options.